ESG
-
Important Results and Sustainability Performance in2024
-
Words from the Management
-
Sustainable Management
-
Sustainable Governance
-
Sustainability and Innovation
-
Environmental Sustainability
-
Common Prosperity and Growth
-
Download Report
-
Interaction
-
Multimedia

Risk Management
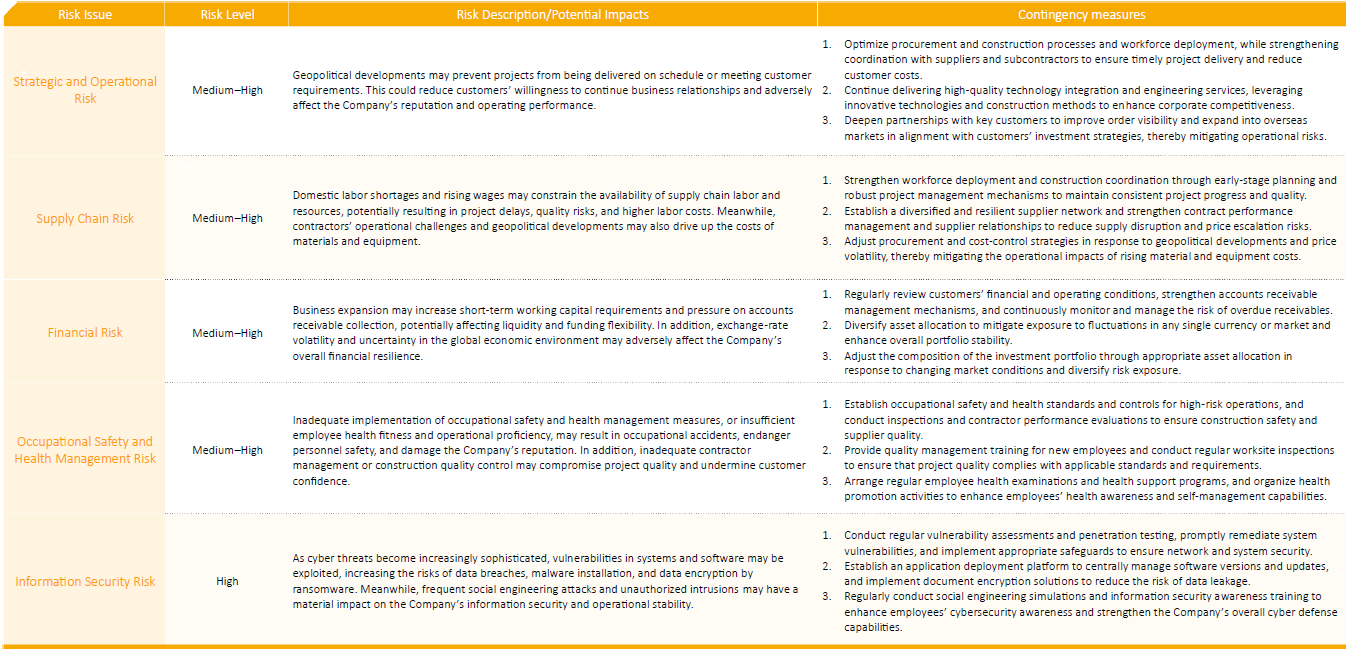
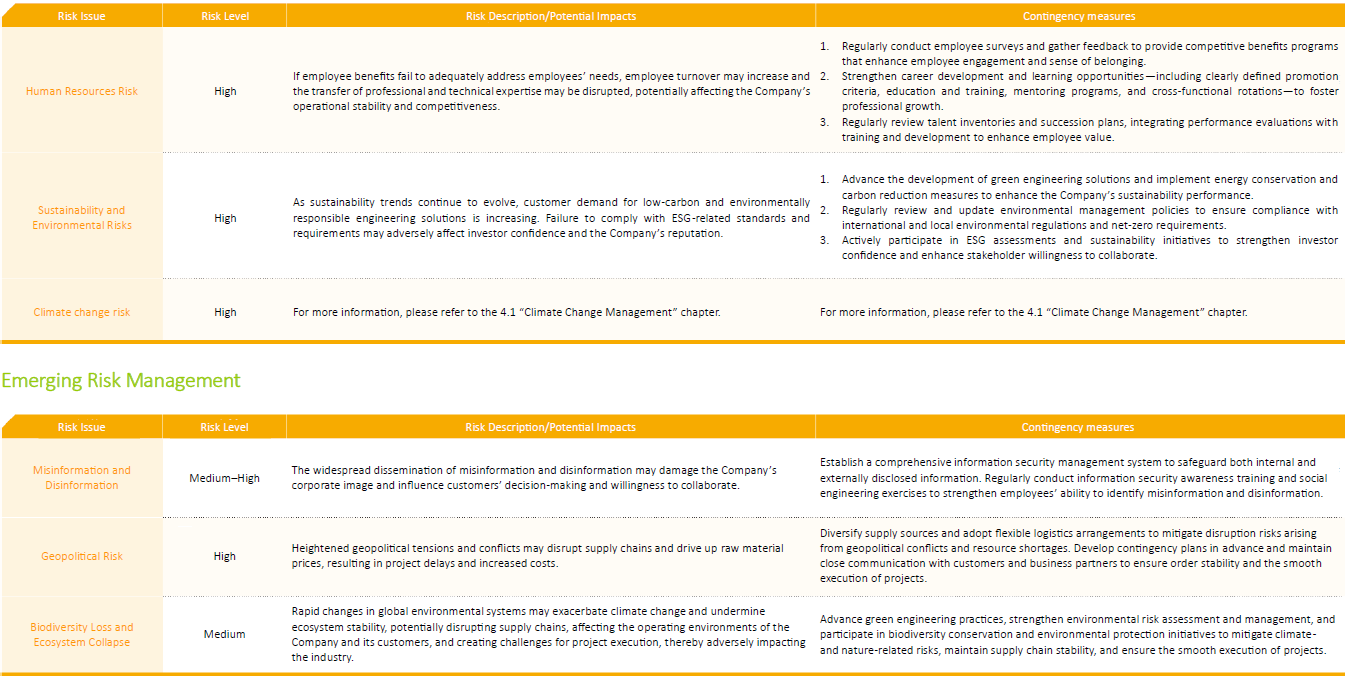
In response to the rapidly evolving business environment and global risk landscape, Acter places sound governance at the core of its operations and has established a robust risk management framework. We continuously monitor internal and external issues and changes in the operating environment to ensure business continuity and safeguard stakeholder interests.
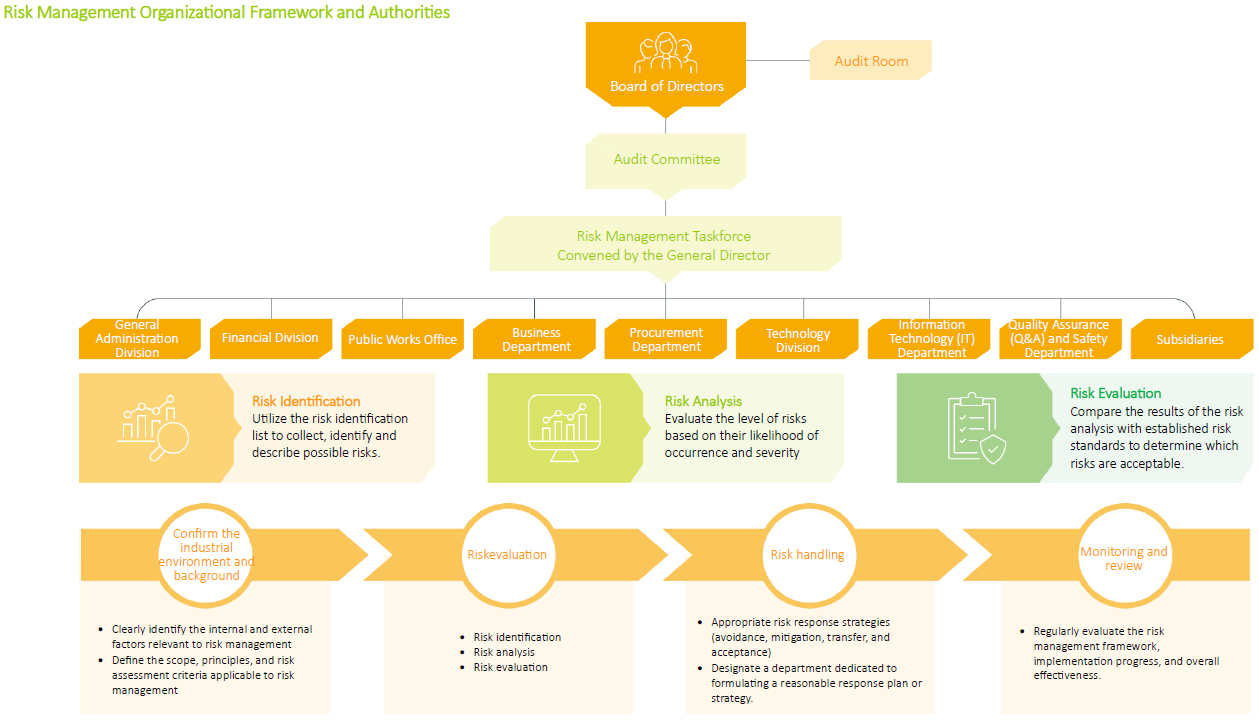
The Board of Directors is Acter’s highest governing body for risk management. In alignment with the Company’s overall business strategy and industry developments, the Board approves risk management policies and material resolutions and assumes ultimate oversight responsibility. Acter has established a Risk Management Task Force that conducts comprehensive analyses and assessments of various operational risks and emerging risk scenarios each year, formulates corresponding response strategies, and submits an annual risk management report to the Board.Chaired by the President and comprising the heads of each business unit, the Task Force is responsible for promoting risk management initiatives, ensuring the effective operation of relevant mechanisms, and coordinating risk management activities across departments.
We have established a comprehensive risk control mechanism supported by clear organizational responsibilities and cross-departmental communication, coordination, and collaboration. This mechanism provides an integrated line of defense encompassing risk identification, assessment, monitoring, and control. All employees are also responsible for identifying and reporting risks. Any material risk event that may affect the Company’s operations must be immediately reported to the relevant supervisor to prevent or mitigate potential operational impacts.
Risk Management and Response Strategies
Information Security Management
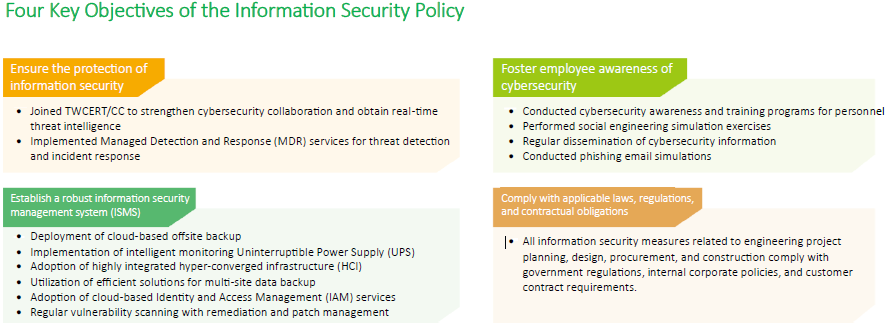
To strengthen cybersecurity resilience and enhance its management mechanisms, Acter has established a comprehensive information security management system. Information security policies and controls are implemented in accordance with the Company’s organizational structure and clearly defined roles and responsibilities, ensuring compliance with applicable laws, regulations, and standards. We regularly conduct cybersecurity incident response drills, employee training, and awareness campaigns to foster a strong security culture across the organization and safeguard the confidentiality, integrity, and availability of the Company’s critical information assets.
Acter has established a dedicated information security function responsible for coordinating cybersecurity policy development and risk management, with a focus on three core areas: information technology (IT), operational technology (OT), and cloud security. The Company safeguards its information assets through robust system protection and data encryption mechanisms. We also actively participate in cybersecurity threat intelligence-sharing platforms, including TWCERT/CC, to establish proactive early-warning and defense mechanisms for addressing potential cyber threats.
Acter adopts the NIST Cybersecurity Framework (NIST CSF) as the foundation of its cybersecurity management system and has implemented a Zero Trust Architecture, under which all access to critical systems and resources is subject to identity authentication and authorization. The Company also employs a multi-layered defense-in-depth approach, including advanced persistent threat protection and endpoint monitoring, to comprehensively enhance its cybersecurity capabilities.